Crypto email marketing in 2026 is the practice of turning wallet users into opted-in subscribers and sending them the messages a public feed handles badly, and it works through five levers: an honest reason to subscribe, an authenticated marketing subdomain, event-driven messages, strict suppression of non-openers and measurement by engagement rather than list size. Each lever answers one of two problems specific to this sector.
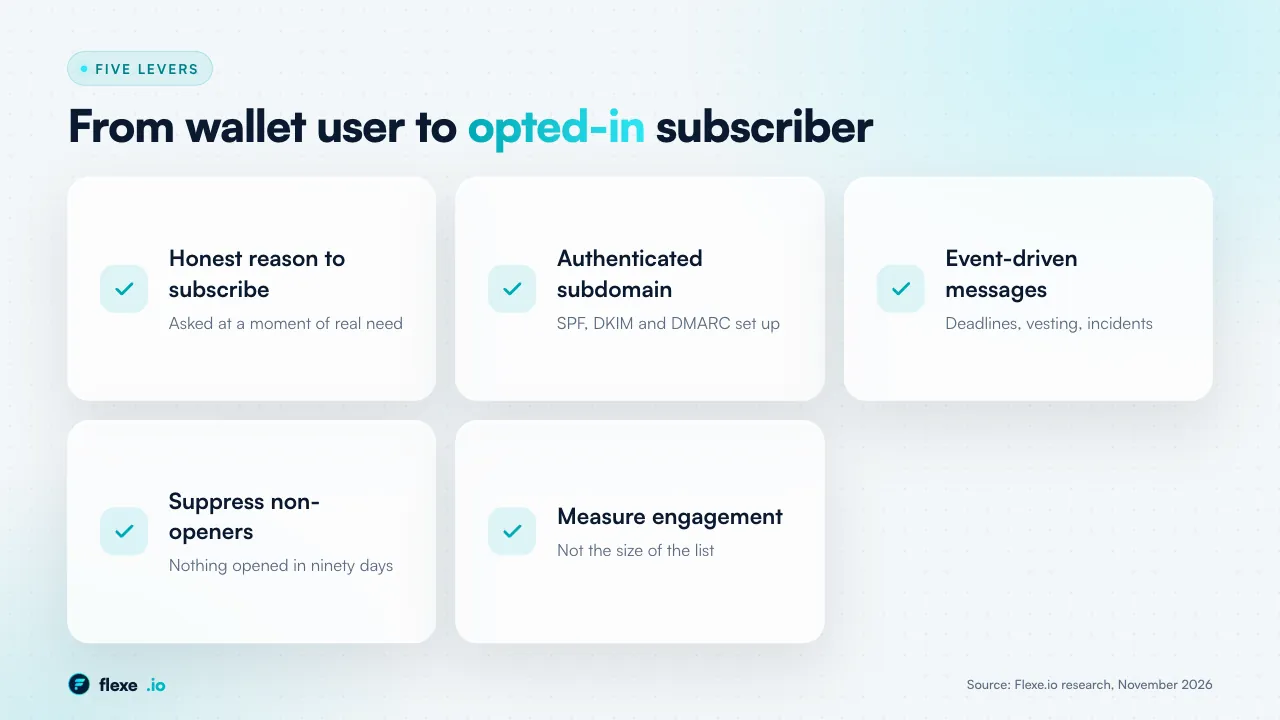
The customer arrives as a wallet address, and a wallet address cannot be emailed, so the list has to be built deliberately. The moment you ask for an address, you are asking a privacy-conscious audience to give up the thing they came here to avoid. The second constraint is deliverability: mailbox providers treat crypto language with suspicion. Both problems are solvable, and both are usually discovered after the first send.
Checked on 10 November 2026 against the current DMARC standard, Google’s sender guidelines and the September 2026 Trezor newsletter incident.
What is email marketing for crypto projects?
It is the owned channel that reaches a specific person and persists. A Telegram announcement reaches whoever is looking at that moment; an email reaches one named recipient and stays in the inbox. That makes email the right channel for anything a holder would be angry to have missed: vesting dates, governance deadlines, security incidents, migration steps and changes that affect funds.
It is a poor channel for the things crypto teams most often use it for. Price commentary and hype belong in the feed, where they cost nothing to ignore, not in an inbox where they train the recipient to stop opening. Email works as the second half of a pair with your public channels: how we plan owned channels.
Crypto email marketing: the key tactics
1. Ask for the address at the point of a real need
Offer something that is worth an address, at a moment when the user has a reason to want it. The exchange has to be honest: a newsletter nobody asked for is not a reason, while a notification the user actually needs is. Governance outcomes, token release schedules, incident notices and product changes are things holders genuinely want to know and cannot reliably get from a feed.
- Ask after a first transaction or a governance vote, not on arrival.
- Say precisely what you will send and how often. Vagueness costs more subscribers than frequency does.
- Never make the address a condition of a reward. That produces the same population as an open airdrop: addresses that exist to collect and never open.
- Keep wallet and email identity linked but separable. The user should be able to leave the list without leaving the product.
- Metric to watch: the share of new subscribers who open anything in their first month.
2. Authenticate and separate the sending domain
Before the first campaign you need a marketing subdomain kept apart from the domain that sends security alerts, SPF, DKIM and DMARC configured and verified, a working unsubscribe header, and a return path that resolves. Content only starts to matter after a message passes those checks, and a message that fails them is filtered regardless of what it says. DMARC itself became an IETF standard in May 2026 with RFC 9989, which replaces RFC 7489, keeps existing v=DMARC1 records valid and drops the pct sampling tag, so recheck any record that relies on it.
- Best for: every project, before any volume is sent.
- Why it matters: a filtered campaign sent from the main domain damages transactional delivery too.
3. Build event-driven messages first
Build the emails tied to an event the recipient already cares about, because those justify the address they gave you: a confirmation of what they signed up for, the notice before a governance deadline, the reminder ahead of a vesting date, the message sent when something changes about how funds are handled.
- Best for: token holders, DAO members and users of products that hold funds.
- Metric to watch: click-through on the specific action the message asks for.
4. Suppress the people who never open
Anyone who has not opened anything in ninety days stops receiving campaigns and receives at most one message asking whether they want to stay. Re-sending to people who never open is the cheapest available way to damage delivery for everybody else on the list, because low engagement is the strongest negative signal a mailbox provider has.
5. Segment by what subscribers told you
A small number of segments carry most of the value: people who hold and would act on a deadline, people who signed up before using anything, and people who have gone quiet. Sending the deadline message to everybody is how the quiet segment ends up depressing delivery of the one message that genuinely mattered. Build segments from behaviour you record: a signup tag plus recent opens and clicks is enough.
Resist segmenting by anything you inferred from a wallet. Grouping recipients by holding size or trades turns a mailing list into a profile, which is exactly what this audience avoids.
6. Write the message nobody can miss
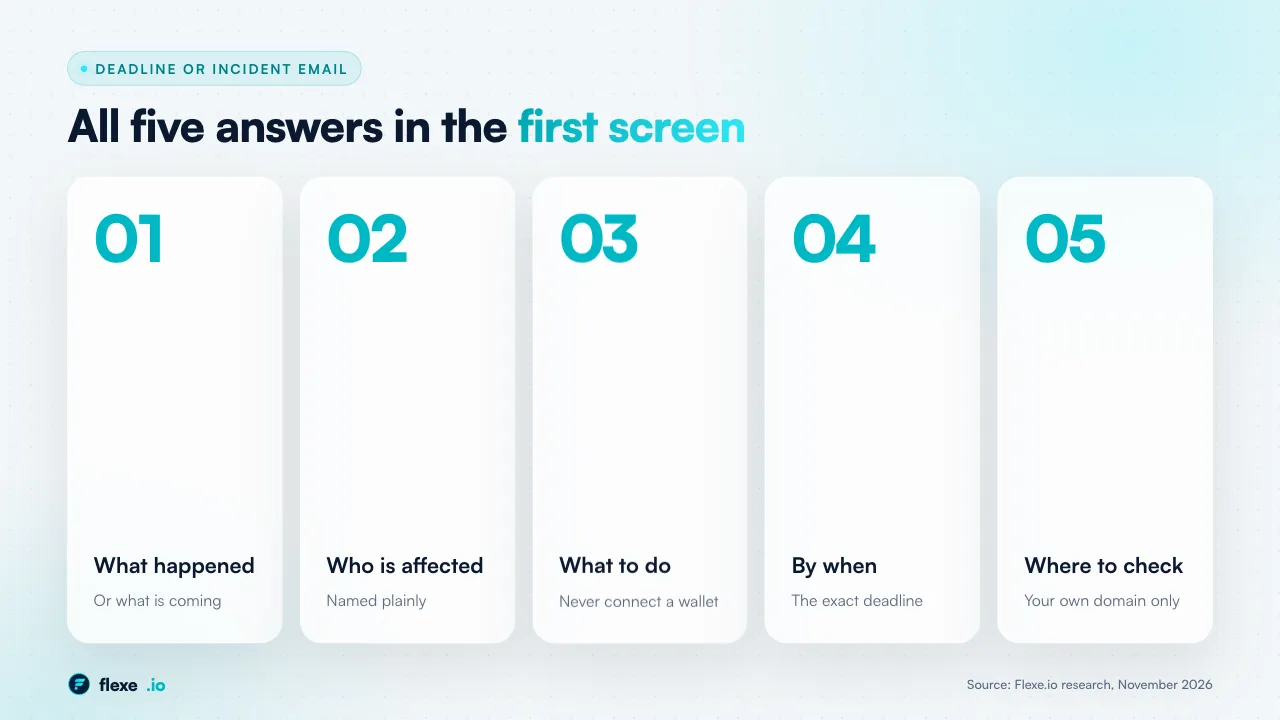
The deadline or incident email has a shape: what happened or what is coming, who is affected, what the recipient has to do, by when, and where to check the authoritative version. Put all of it in the first screen, before any explanation, because the recipient who acts will not scroll and the one who would not scroll is the one you were writing for. The same first-screen rule applies to regular newsletters, which our crypto copywriting service writes to this structure.
Never ask a recipient to connect a wallet from an email, and say on the site and in the message that you will never do so. Every phishing campaign against your holders will imitate this exact message, and the defence is a habit the audience can rely on rather than a warning printed inside the imitation. Link to your own domain only, and to a page that exists before the send.
How to plan it step by step
1. Set up and authenticate a marketing subdomain
Keep operational messages architecturally separate from campaigns, so a security notice can never be filtered because a campaign annoyed somebody.
2. Choose a sending platform you can leave
Whatever platform you send from needs authentication on a domain you control rather than a shared sending domain, per-message event data you can export, suppression rules that survive an import, and a way for the product to trigger operational messages without a marketer in the loop. Ask where the data is stored and what happens to it if you leave, because an export that arrives as a summary rather than as addresses and events is a migration you cannot make. Then limit who can export: the Trezor list left its provider through the API.
3. Confirm every address at signup
A confirmation step costs subscribers at the point of collection and saves the list afterwards, because it removes mistyped addresses and the ones entered by somebody else. For an audience that guards its identity, that record is also the only defensible evidence that consent existed at all. Keep your own copy, with the timestamp, outside the sending platform.
4. Warm the subdomain before volume arrives
Start with the recipients most likely to open, which is usually the people who asked for something specific, and raise volume gradually instead of sending to the whole list on the first day. A new domain sending to thousands of addresses at once is the pattern mailbox providers are built to catch.
5. Test before the first send
Send the campaign to yourself across the providers your recipients use, on a phone and a desktop, and read it in the preview pane. Check that the sender name is recognisable, that the first line makes sense without images loaded and that every link resolves to the page you meant. Then check the plain text version, the unsubscribe link from a logged-out browser and a reply address that a person reads.
6. Set suppression rules alongside the campaigns
Write the ninety-day rule into the platform on the same day the first campaign is built, and test the operational path on its own schedule, not alongside a send.
Why do crypto emails end up in spam?
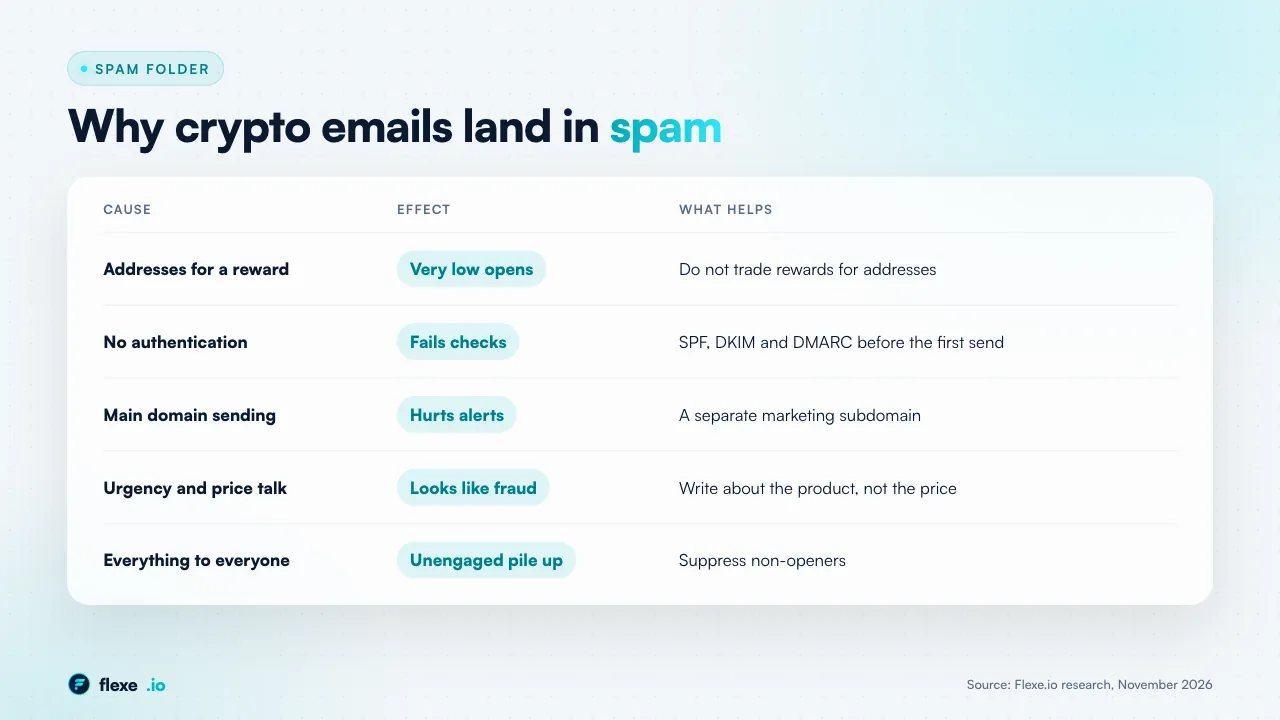
Because the words that describe the product overlap heavily with the words that describe fraud, and because list quality in this sector is unusually poor. A list assembled from a reward campaign will contain a high share of addresses that never open anything.
| Cause | Effect | What helps |
|---|---|---|
| Addresses collected for a reward | Very low open rates drag the whole domain down | Do not trade rewards for addresses at all |
| Authentication not configured | Messages fail basic checks before content matters | SPF, DKIM and DMARC set correctly before the first send |
| Sending from the main domain | A filtered campaign damages transactional delivery too | A separate subdomain for marketing sends |
| Urgency and price language | Pattern-matches to fraud | Write about the product, not the price |
| Sending everything to everyone | Unengaged recipients accumulate | Suppress non-openers rather than re-sending to them |
Mistakes to avoid
- Buying growth with rewards. Addresses collected during a reward campaign look like growth for a quarter and then show up as a falling engagement share.
- Frequency without purpose. A weekly send that exists because the calendar says so teaches the recipient that nothing in it needs opening.
- Selling into an obligation. Treating the address as a channel to sell into rather than an obligation to inform.
- Mixing marketing and operational mail. Getting that line wrong in the direction of convenience turns a delivery problem into a complaint.
The usual failure is not the spam folder but the list itself. Sending less, and only when there is something to act on, is most of the discipline.
Rules on consent, sender identification and unsubscribes apply to a project registered anywhere and sending everywhere, and they do not care that the audience is anonymous. Keep the record of when and how each address was collected, identify the sender in the footer, and honour an unsubscribe on every kind of marketing message; the US CAN-SPAM guide sets 10 business days. Decide which messages are operational and can be sent to everyone affected, and which are marketing and go only to people who agreed, because it is the complaint that mailbox providers act on.
Plan the response to a leak in advance
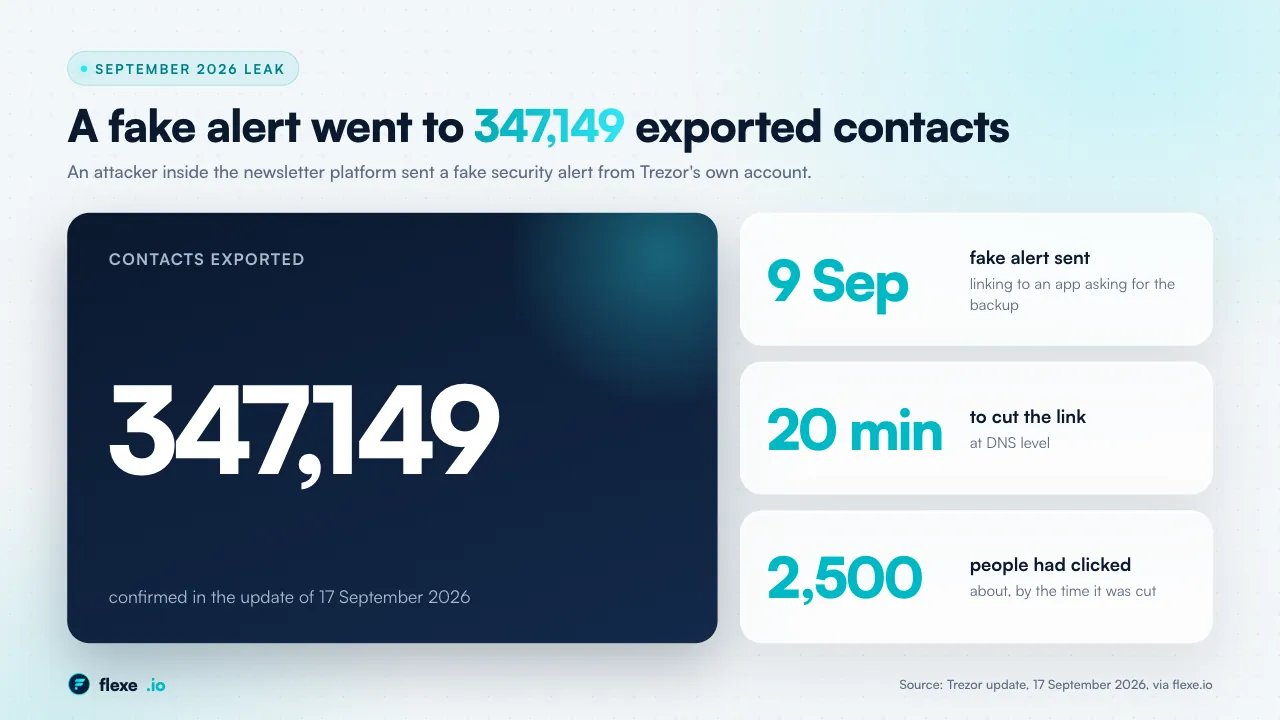
Assume the list will eventually be exposed, by a vendor, an export or a former contractor. On 9 September 2026 an attacker inside Brevo, the newsletter platform Trezor uses, sent a fake security alert from Trezor’s own account to roughly 347,000 opt-in subscribers, linking to an app that asked for the wallet backup. In an update of 17 September 2026 Trezor said Brevo confirmed 347,149 contacts were exported.
Tell the affected recipients yourself, first, saying what was in the file and what was not; the alternative is that they learn about it from the phishing message that arrives afterwards. Keep the stored data thin enough that a leak is survivable: the address, the confirmation record and what they subscribed to, without balances, transaction history or anything tying the address to a specific holding.
Because Brevo routed every link through Trezor’s domain, Trezor cut the link at DNS level within 20 minutes, and about 2,500 people had clicked by then. After any exposure, expect messages imitating yours within days. Post a short statement on the site, repeat the rule that you never ask for a wallet connection by email, and give one address where recipients can check whether a message is genuine. Then keep sending on the normal schedule, because silence leaves the imitators as the only voice. The same trust logic runs through how we structure community programmes.
How to measure results
Open rate has become unreliable across the industry because of privacy protections that pre-fetch images, so read it as a trend rather than a level. The figures worth reporting for crypto email marketing are these:
- Click-through on the specific action each message asks for.
- The share of the list that has opened anything in the last ninety days.
- Unsubscribe rate by campaign type.
- Delivery rate by mailbox provider.
A list that grows while ninety-day engagement falls is getting worse, not better, and most reports leave that number out. Track it monthly by acquisition source; one source usually turns out to supply the subscribers who never open.
Frequently Asked Questions
Does email marketing work for crypto projects?
Yes, for a narrow set of uses. Email is the right channel for anything a holder would be angry to have missed, such as vesting dates, governance deadlines, security notices and changes that affect funds. It is a weak channel for price commentary, market updates and general hype, which belong in the public feed where they cost nothing to ignore.
How do you collect emails when users connect with a wallet?
Ask at a moment of genuine need, such as after a first transaction or a governance vote, and state exactly what will be sent and how often. Never trade a reward for an address, because that produces a list that never opens. Keep wallet and email identity linked but separable, so a user can leave the list without leaving the product.
Why do crypto emails land in spam?
Crypto emails land in spam because the vocabulary overlaps with fraud language and because crypto lists often contain many addresses collected for rewards that never open anything. Low engagement is the strongest negative signal a mailbox provider uses. Missing SPF, DKIM and DMARC, urgency and price language, and re-sending to non-openers make it worse.
Should crypto marketing emails come from the main domain?
No. Use a separate subdomain for marketing sends, so that a filtered campaign does not damage delivery of transactional messages such as security alerts. Authenticate that subdomain with SPF, DKIM and DMARC before the first send, and warm it gradually, starting with the recipients most likely to open rather than the whole list on day one.
What metrics matter in crypto email marketing?
The metrics that matter are click-through on the specific action, the share of the list that opened anything in the last ninety days, unsubscribe rate by campaign type and delivery rate by mailbox provider. Open rate is unreliable because privacy protections pre-fetch images, so read it only as a trend. A growing list with falling engagement is getting worse.
What should a crypto project do if its email list leaks?
Tell subscribers yourself, first, what the file held and what it did not, then post a short notice on the site and repeat that you never ask for a wallet backup or connection by email. Suspend the sending account and cut tracked link domains. Trezor did this in September 2026 and held clicks on the phishing link to about 2,500 people.
If you would rather have this run for you, see our content production service.